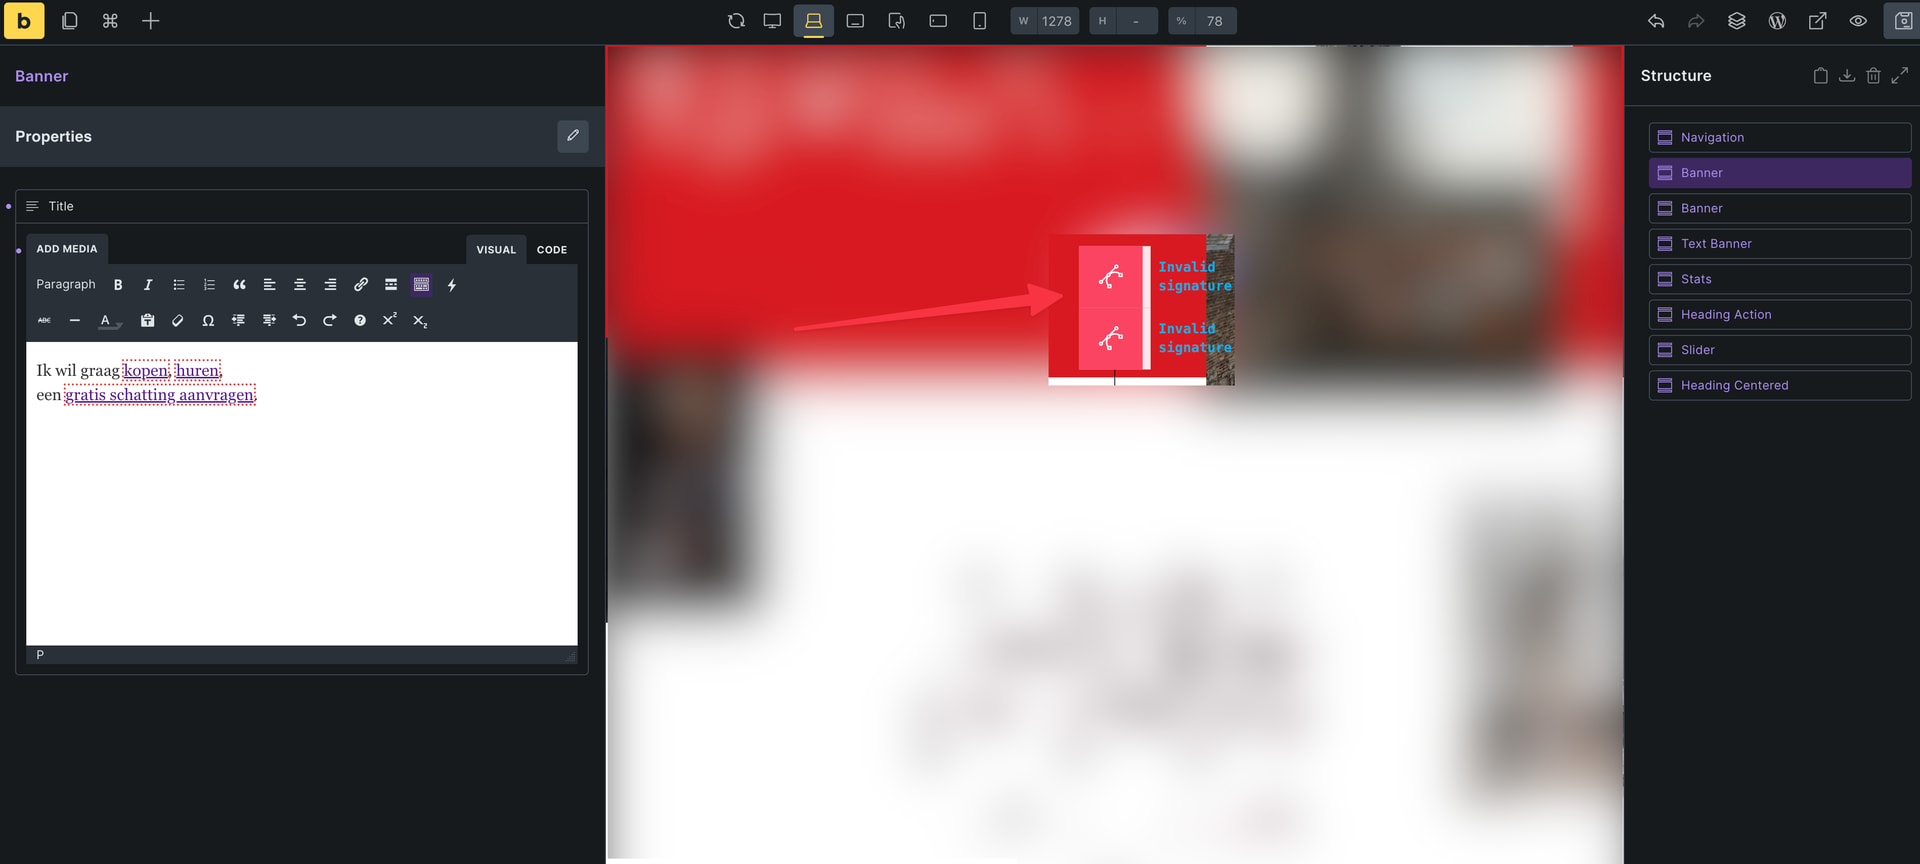
My clients can only add/move/delete components, and edit their props.
This all works fine and super efficient, however, if a component has an SVG in it which uses code, it shows: “Invalid signature“.
Which means that my clients can’t add or duplicate components that have an SVG or code in them.
Only when I give the customer full access they can duplicate or insert components with an SVG inside, without the annoying warning. But I am not giving my customers full access for a reason.
Is this a bug, or is there a work around? It would be a shame to revert my components back to regular blocks. I don’t want my customers to mess around in the structure panel in order to find the code to sign it.
My proposal: don’t require signing when you add or duplicate a component. Because that code was already signed by the developer who made the component.
Hope my description makes sense
ps. I am new to Bricks and it’s awesome so far!
Hopefully you guys can help me out.
Browser: Dia Browser / Chromium 143.0.7499.194 WordPress: 6.9 OS: macOS
I suppose the user doesn’t have the capability to edit the component enabled, right? Because if he does, then you can just enable code execution for his role.
However, I can replicate the problem if user can’t actually edit the component. Before I discuss this internally or create an internal report, can you just confirm if it works on the front end if the user duplicates the component? I guess it should, and the problem is only on the backend, right?
Overall, I think this makes sense. If user duplicates it, no need to sign it again.
Hi Matej, thank you for the warm welcome and quick reply!
Lovely community!
I suppose the user doesn’t have the capability to edit the component enabled, right? Because if he does, then you can just enable code execution for his role.
Yes, if you give the user permission to edit components he could dive in the component settings, and sign it.
But this does not seem preferable for non-techies since it requires navigating into the structure panel to find the code element.
Before I discuss this internally or create an internal report, can you just confirm if it works on the front end if the user duplicates the component?
I just tested it, it does seem to render on the front-end. I don’t remember if it did yesterday, but I suppose so.
Overall, I think this makes sense. If user duplicates it, no need to sign it again.
Yeah, I think it’s very secure because the user can’t change anything to the component itself. Especially when you don’t give them the permission to edit components.